



Microsoft 365
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.
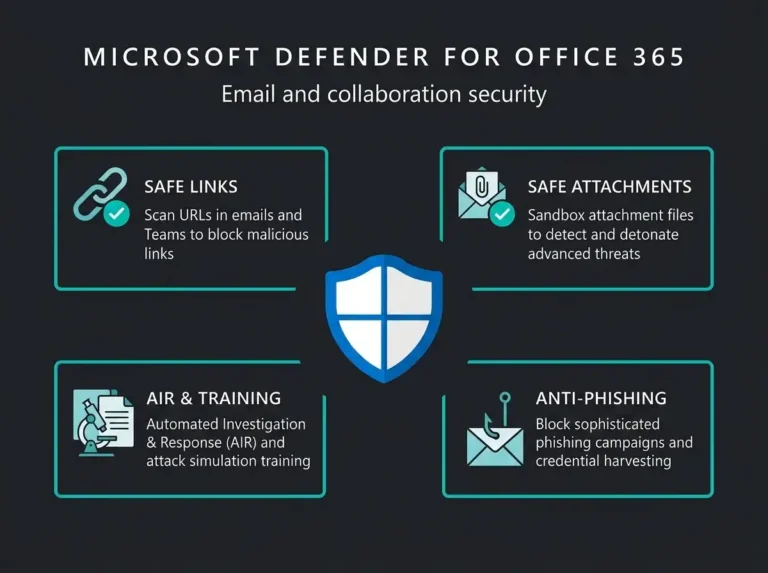
Microsoft Defender for Office 365 for SMBs
Microsoft Defender for Office 365 adds Safe Links, Safe Attachments, anti-phishing, and response tooling on top of Microsoft 365 baseline email security.
Read more
Spear Phishing Prevention: Protection Strategies for Microsoft 365
Spear phishing prevention for Microsoft 365: Defender for Office 365, DMARC, MFA, user reporting, and response steps that actually reduce risk.
Read more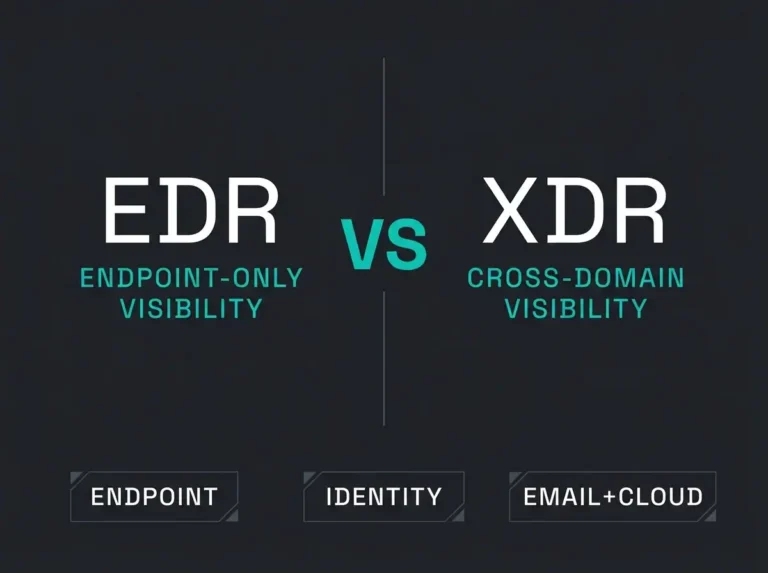
XDR vs EDR: What’s the Difference?
XDR vs EDR explained for Microsoft-focused SMBs: scope, use cases, licensing context, and how to choose the right detection model.
Read more
Benefits of EDR for Small Business
Benefits of EDR for small business: faster detection, containment, visibility, and stronger Microsoft security operations.
Read moreNew Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.