



Microsoft Security Insights
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.
The Defender for Office 365 Settings Most SMBs Get Wrong
Defender for Office 365 baseline configuration guide for SMBs: the settings most teams get wrong and how to fix them.
Read more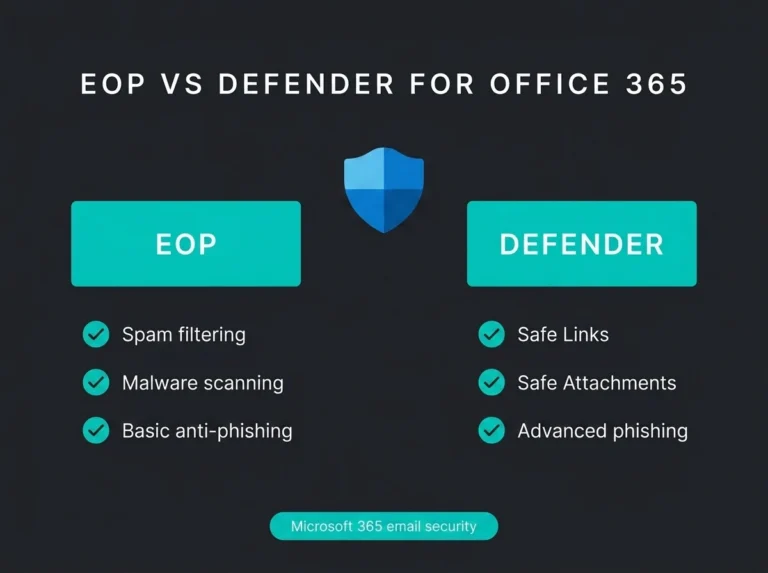
Exchange Online Protection vs Defender for Office 365: Which Do You Need?
Exchange Online Protection vs Defender for Office 365: what each includes, where EOP stops, and when SMBs should pay for stronger email security.
Read more
What Is Vishing? Voice Phishing Explained
Learn what vishing is, how voice phishing attacks work, and what Microsoft-focused SMBs should do to stop phone-based social engineering.
Read more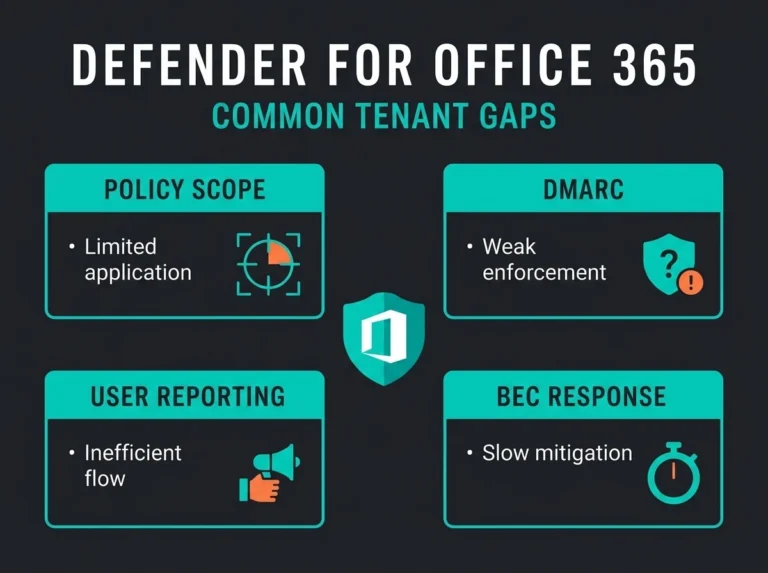
What Defender for Office 365 Misses: Findings from Real Assessments
Defender for Office 365 gaps usually come from policy, DMARC, and response issues. Here is what Falconer finds in real email security assessments.
Read moreNew Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.