



Microsoft 365
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.
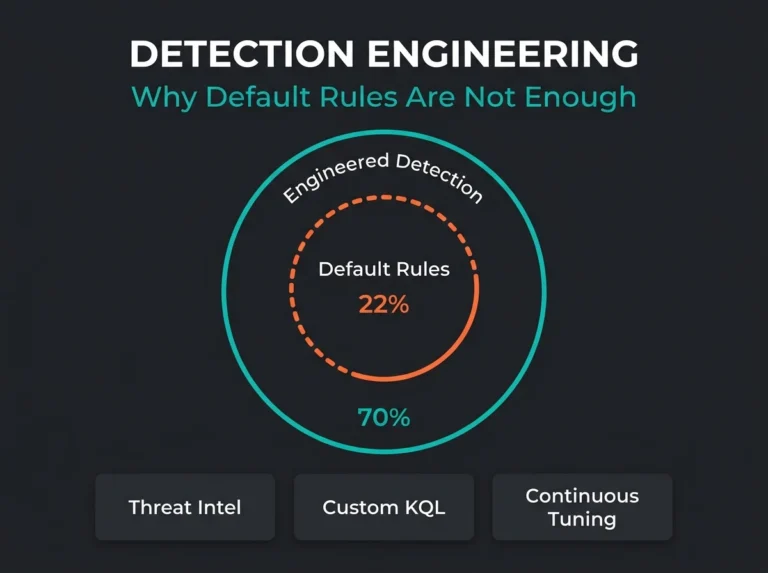
Detection Engineering for Microsoft Sentinel: Why Default Rules Are Not Enough
Default Sentinel rules cover only 22% of MITRE ATT&CK techniques. Learn what detection engineering is and what managed providers do differently.
Read more
10 Microsoft 365 Security Defaults That Are Quietly Exposing Your Company
Discover 10 Microsoft 365 default settings creating security risks in your tenant and how to fix them before attackers exploit them.
Read more
CISO as a Service: What SMBs Need to Know
CISO as a Service gives SMBs expert security leadership without a full-time hire. Learn what a vCISO does, costs, and how to choose.
Read more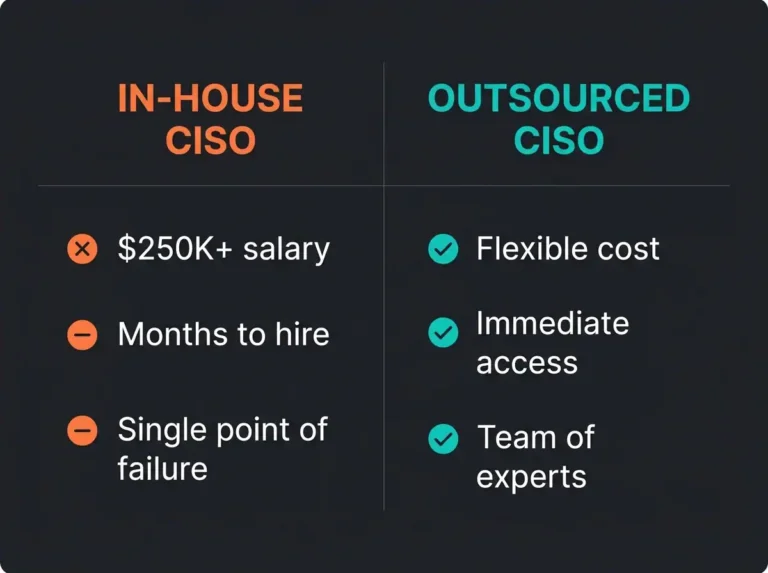
Outsourced CISO: Pros, Cons, and Costs
What an outsourced CISO costs, what they do, and when your company needs one. Compare pricing, pros, cons, and delivery models.
Read moreNew Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.