



Microsoft Security Insights
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.

Cloud SIEM vs On-Prem SIEM: Pros and Cons for SMB Security Teams
Cloud SIEM usually wins for SMBs because it scales faster and reduces platform overhead, but on-prem SIEM still has a place in legacy and
Read more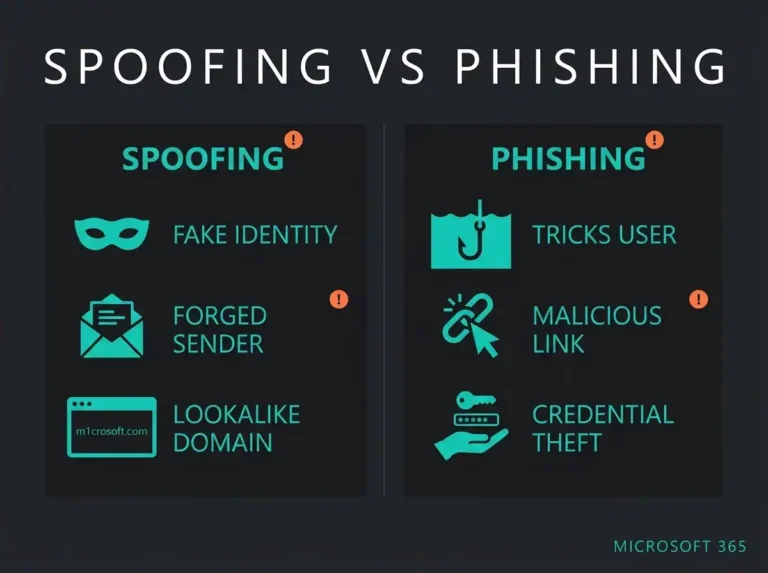
Spoofing vs Phishing: What Microsoft 365 Admins Need to Know
Email threats often get bucketed together, but spoofing vs phishing is not one problem. Knowing the difference changes what you fix first in Microsoft
Read more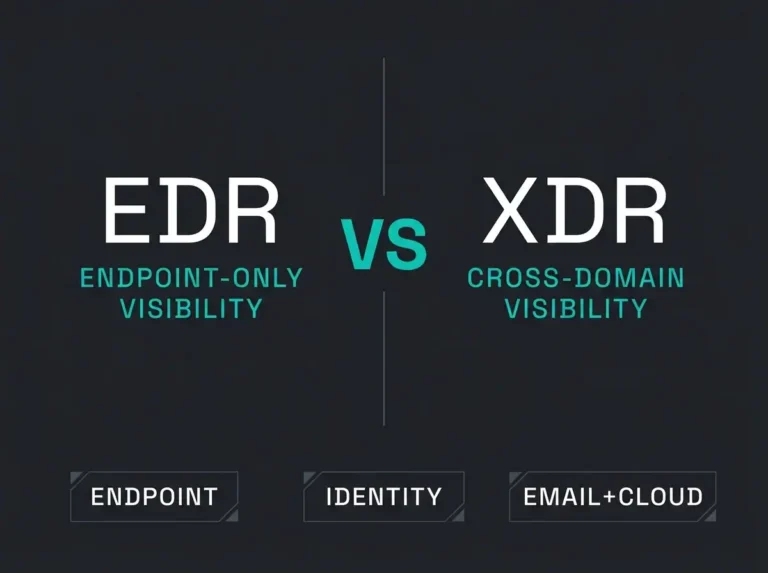
XDR vs EDR: What’s the Difference?
XDR vs EDR explained for Microsoft-focused SMBs: scope, use cases, licensing context, and how to choose the right detection model.
Read more
Benefits of EDR for Small Business
Benefits of EDR for small business: faster detection, containment, visibility, and stronger Microsoft security operations.
Read moreNew Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.