



Microsoft Security Insights
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.
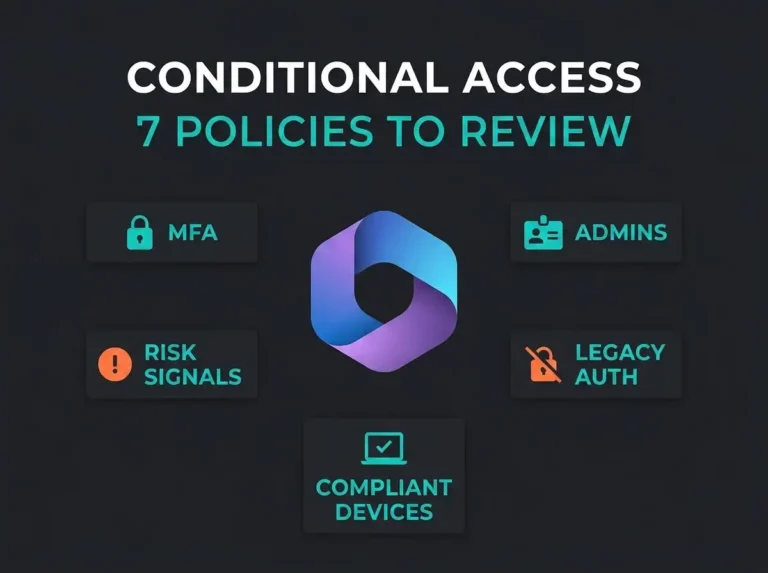
7 Conditional Access Policies Every M365 Tenant Should Review
Most Microsoft 365 tenants don’t get breached because Entra ID lacks security controls. They get breached because the right Conditional Access policies were never
Read more
Azure Security Assessment: What We Check and Why
Your company runs workloads in Azure. A handful of VMs, some storage accounts, maybe a database or two. Then someone in leadership asks how
Read more
10 Microsoft 365 Security Defaults That Are Quietly Exposing Your Company
Discover 10 Microsoft 365 default settings creating security risks in your tenant and how to fix them before attackers exploit them.
Read more
What Is a vCISO? Virtual CISO Explained for SMBs
A virtual CISO provides executive-level cybersecurity leadership on a fractional basis. Learn what a vCISO does, costs, and when SMBs need one.
Read moreNew Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.