



Microsoft Sentinel
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.
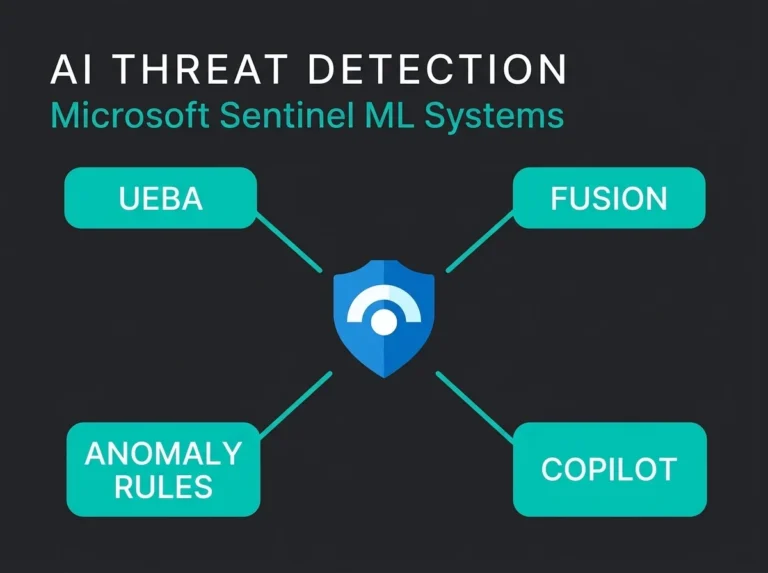
AI-Powered Threat Detection: How Microsoft Sentinel Uses Machine Learning
How Microsoft Sentinel uses UEBA, Fusion, anomaly rules, and Security Copilot for AI threat detection. Practical guide for SMBs and MSPs.
Read more
5 Default Sentinel Rules That Generate Nothing But Noise (And What We Replace Them With)
Five default Microsoft Sentinel analytics rules that generate the most false positives, and what Falconer Security replaces them with.
Read more
Deploying Sentinel for a New Client: Our MSSP Onboarding Checklist
Complete MSSP checklist for deploying Microsoft Sentinel. Covers Lighthouse, GDAP, workspace setup, connectors, and cost controls.
Read more
Cyber Insurance Requirements: What Security Controls Do Insurers Require?
Learn the 8 security controls cyber insurers require in 2026, from MFA and EDR to SIEM and incident response plans.
Read moreNew Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.