



Microsoft Security Insights
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.
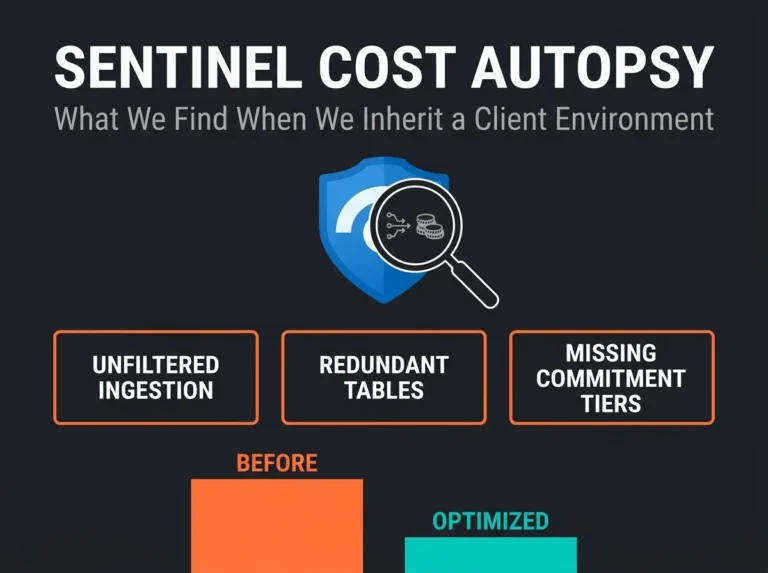
What We Find When We Inherit a Client’s Sentinel: A Cost Autopsy
Falconer Security reveals the 5 most common Sentinel cost failures in inherited MSSP workspaces and how to fix them.
Read more
What Is a Managed Security Service Provider (MSSP)?
What is a MSSP? Your IT team already covers everything from onboarding laptops to troubleshooting the VPN. Hand them “detect and respond to sophisticated
Read more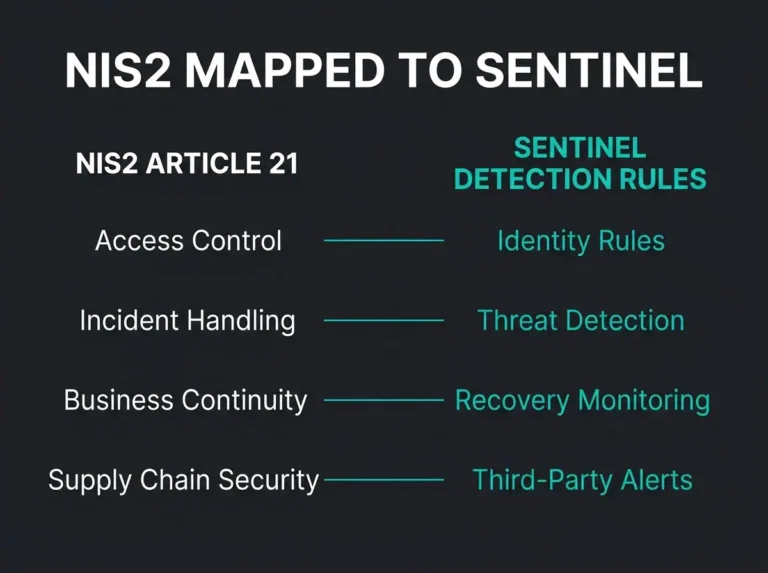
NIS2 Article 21 Mapped to Microsoft Sentinel: What Detection Requirements Actually Mean
Complete mapping of all 10 NIS2 Article 21 requirements to Microsoft Sentinel capabilities. Learn what Sentinel covers, where gaps remain, and how to configure
Read more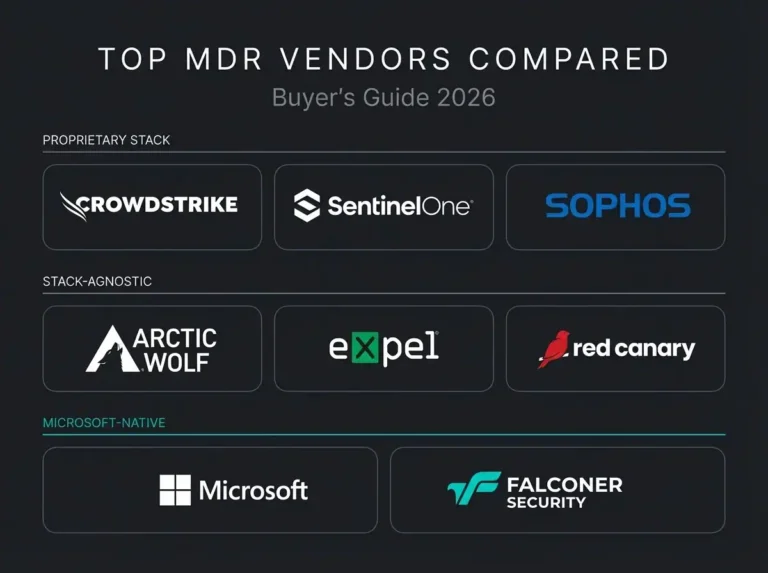
Top MDR Vendors Compared: Buyer’s Guide for 2026
Compare top MDR vendors including CrowdStrike, Arctic Wolf, Sophos, and Microsoft Defender Experts. Honest buyer's guide with pricing and evaluation criteria.
Read moreNew Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.