



Managed Sentinel
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.
Managed Sentinel Provider: What to Expect
What to expect from a managed Sentinel provider, including onboarding, detection tuning, response workflows, and cost control.
Read more
Cloud SIEM vs On-Prem SIEM: Pros and Cons for SMB Security Teams
Cloud SIEM usually wins for SMBs because it scales faster and reduces platform overhead, but on-prem SIEM still has a place in legacy and
Read more
Cloud-Native SIEM: Why It Matters for Modern Security
Your on-premises SIEM was designed for a world where servers sat in your data center, users worked from the office, and security logs came
Read more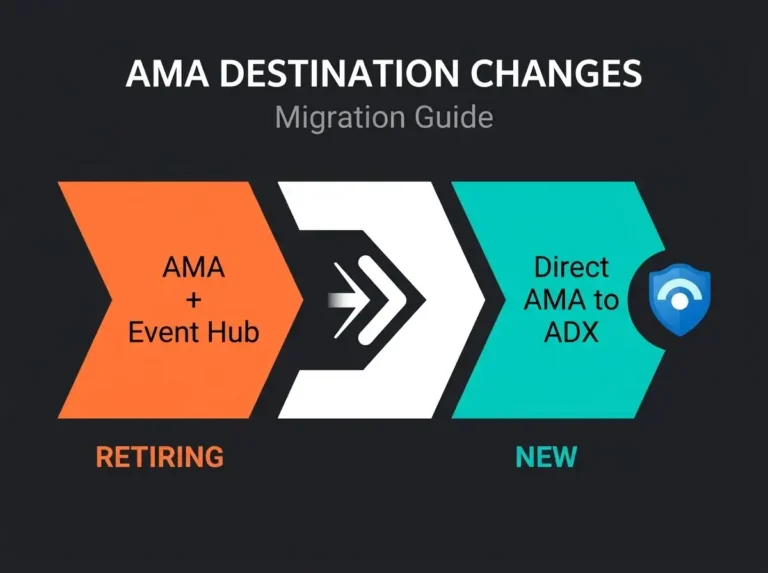
AMA Destination Changes: What Your Sentinel Deployment Needs to Know
Microsoft is retiring AMA Event Hub and Storage destinations in July 2026. Learn how the new direct-to-ADX ingestion works and how to plan your
Read moreNew Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.