



Microsoft Security Insights
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.
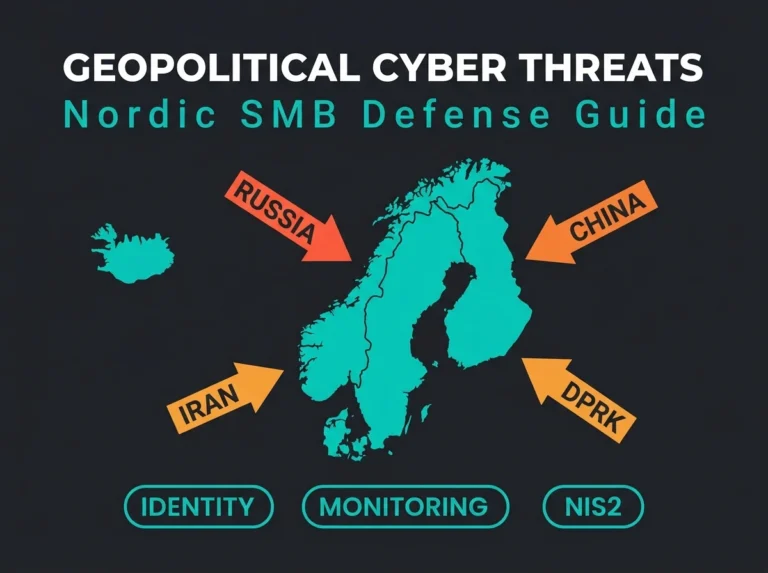
Geopolitical Cyber Threats in 2026: What Nordic SMBs Need to Know
Nation-state cyber threats now target Nordic SMBs. Learn which threat actors operate in the Nordics and how to defend your business.
Read more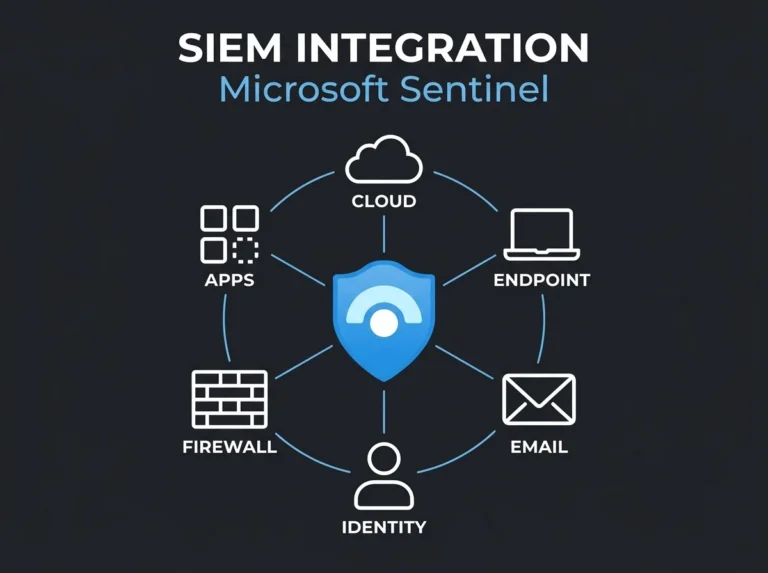
SIEM Integration: Connecting Your Security Stack to Microsoft Sentinel
Learn how to integrate your security stack with Microsoft Sentinel. Covers data connectors, deployment order, cost optimization, and NIS2 compliance.
Read more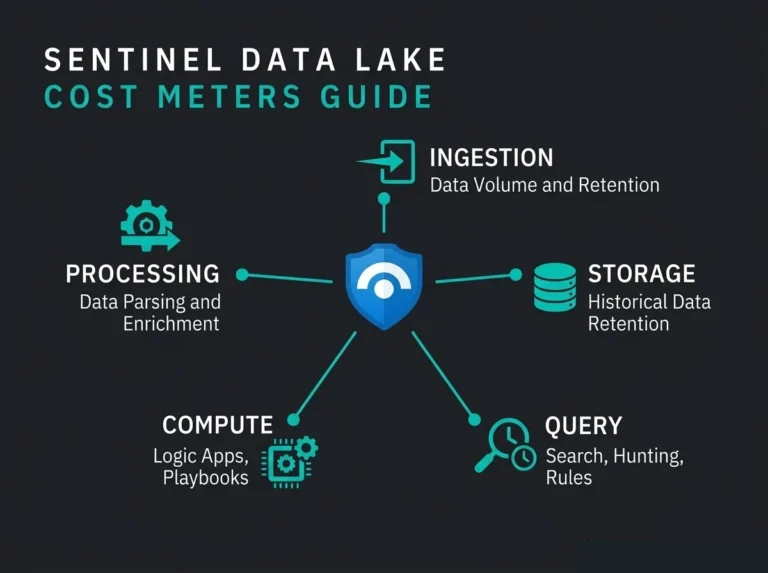
Microsoft Sentinel Data Lake Meters: A Cost Management Guide
Understand the five Microsoft Sentinel data lake meters, what drives each cost, and how to monitor and control spending.
Read more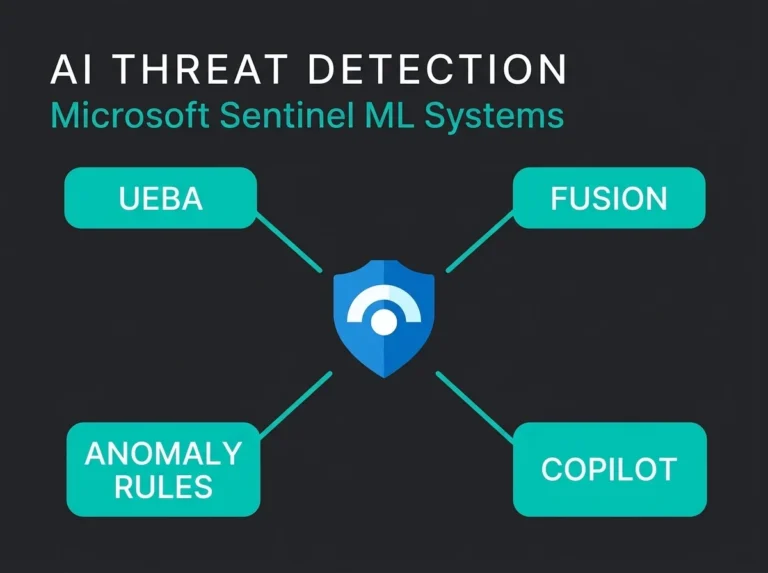
AI-Powered Threat Detection: How Microsoft Sentinel Uses Machine Learning
How Microsoft Sentinel uses UEBA, Fusion, anomaly rules, and Security Copilot for AI threat detection. Practical guide for SMBs and MSPs.
Read moreNew Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.