



Microsoft Security Insights
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.
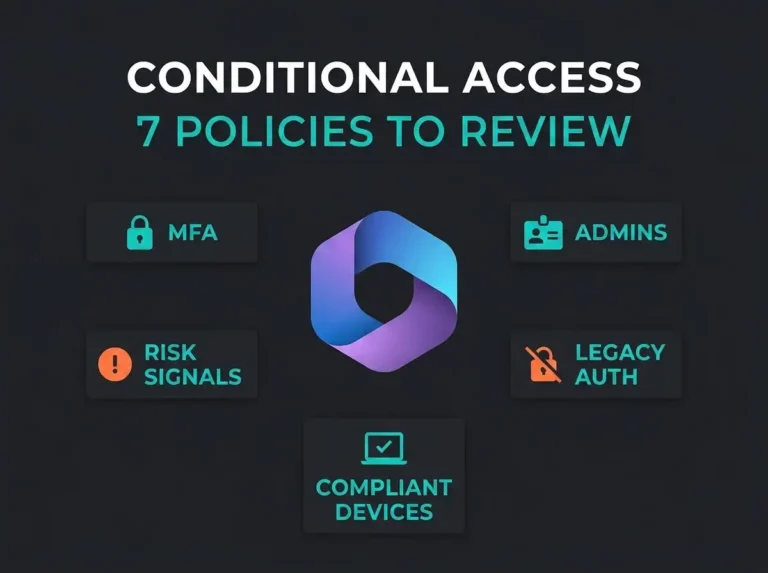
7 Conditional Access Policies Every M365 Tenant Should Review
Most Microsoft 365 tenants don’t get breached because Entra ID lacks security controls. They get breached because the right Conditional Access policies were never
Read more
SOC as a Service: Complete Guide for SMBs
What SOC as a Service means for SMBs, how it differs from managed SIEM and MDR, and how to evaluate whether an outsourced SOC
Read more
SIEM Implementation: Step-by-Step Guide for Microsoft Sentinel Deployments
A practical SIEM implementation guide for Microsoft Sentinel covering planning, connectors, tuning, retention, automation, and post-deployment review.
Read more
Managed SOC Services: What’s Included?
Managed SOC services should include 24/7 monitoring, triage, investigation, response support, and tuning across Microsoft Defender XDR and Sentinel.
Read moreNew Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.