



Microsoft Security Insights
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.
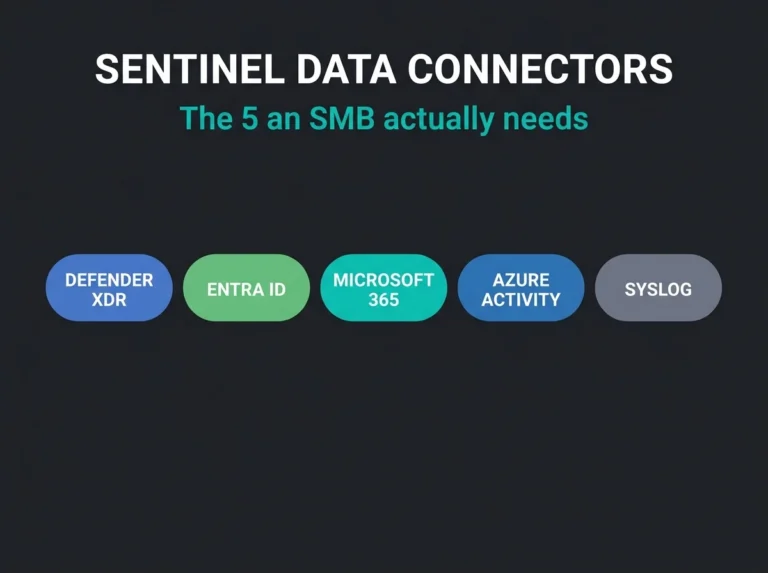
The Only 5 Microsoft Sentinel Data Connectors an SMB Actually Needs
A practical Microsoft Sentinel rollout for SMBs starts with five connectors: Defender XDR, Entra ID, Microsoft 365, Azure Activity, and Syslog via AMA.
Read more
MSSP vs SOC: Which Security Model Fits Your Business?
MSSP vs SOC explained for SMBs: ownership, cost, response depth, and which model fits your business.
Read more
Virtual CISO Services: Complete Guide for SMBs
If your business needs security leadership but not a full-time chief information security officer, virtual CISO services can close the gap. That matters more
Read more
How We Tune Sentinel Rules Across Multiple Client Tenants
How MSSPs tune Microsoft Sentinel rules across client tenants without drowning in false positives or weakening real detections.
Read moreNew Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.