



Microsoft Security Insights
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.
Security Operations Center Framework: What SMBs Actually Need
SOC framework guide for SMBs covering NIST, ATT&CK, detection workflows, response playbooks, and Microsoft security operations design.
Read more
SOC Optimization in Microsoft Sentinel: What It Gets Right and Wrong
SOC optimization in Microsoft Sentinel helps reduce waste and close detection gaps, but it still needs human review before you trust the output.
Read more
24/7 SOC Service: What Good Coverage Actually Looks Like
24/7 SOC service explained: what continuous monitoring should include, what to ask providers, and when SMBs actually need it.
Read more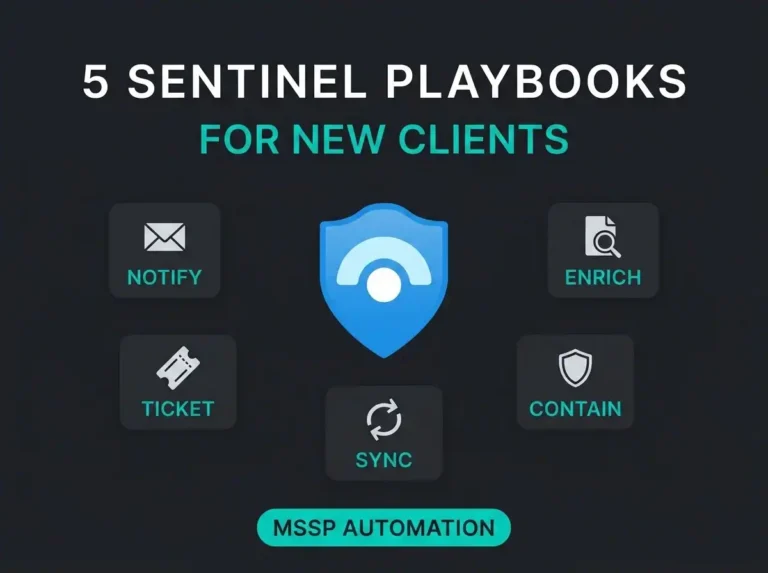
The 5 Microsoft Sentinel Playbooks We Deploy for New Clients First
Five Microsoft Sentinel playbooks we deploy first to speed up triage, enrichment, containment, and case handling for new clients.
Read moreNew Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.