



Microsoft Security Insights
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.

Managed SOC for MSPs: When to Partner Instead of Build
Managed SOC for MSPs: how to choose a SOC partner, define responsibilities, and scale Microsoft-focused security services.
Read more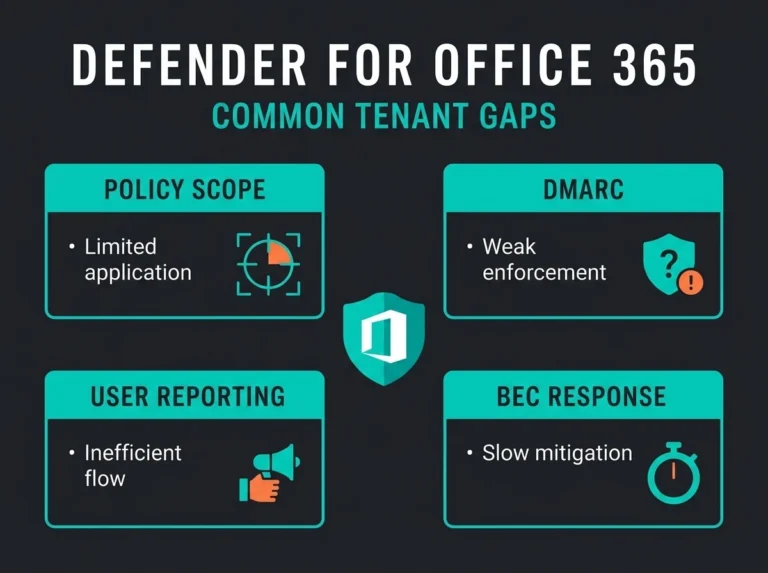
What Defender for Office 365 Misses: Findings from Real Assessments
Defender for Office 365 gaps usually come from policy, DMARC, and response issues. Here is what Falconer finds in real email security assessments.
Read more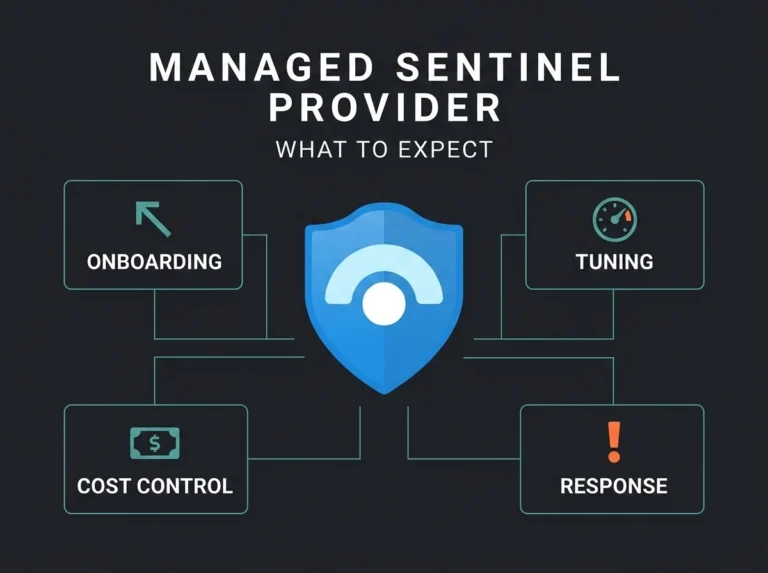
Managed Sentinel Provider: What to Expect
What to expect from a managed Sentinel provider, including onboarding, detection tuning, response workflows, and cost control.
Read more
Microsoft Purview for SMBs: Data Security and Compliance Guide
What Microsoft Purview actually does for SMBs, which features matter first, and how to roll out labels, DLP, and audit controls without breaking user
Read moreNew Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.