



NIS2
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.
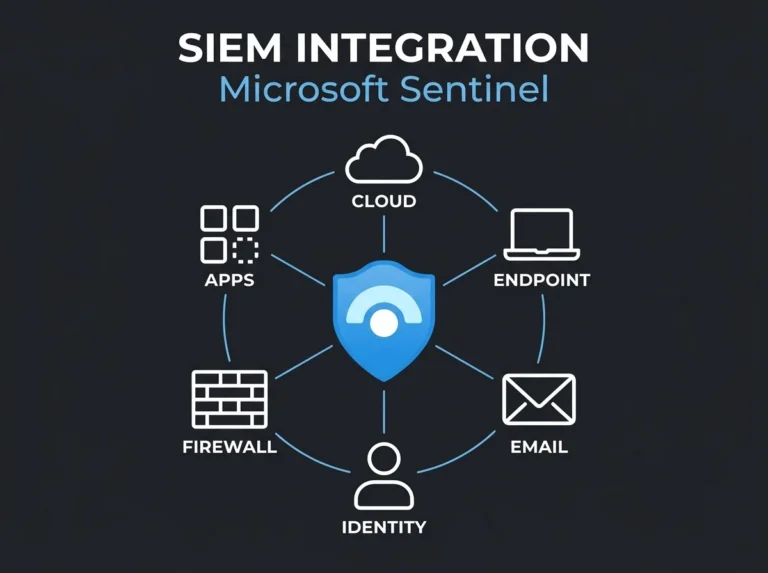
SIEM Integration: Connecting Your Security Stack to Microsoft Sentinel
Learn how to integrate your security stack with Microsoft Sentinel. Covers data connectors, deployment order, cost optimization, and NIS2 compliance.
Read more
Cyber Insurance Requirements: What Security Controls Do Insurers Require?
Learn the 8 security controls cyber insurers require in 2026, from MFA and EDR to SIEM and incident response plans.
Read more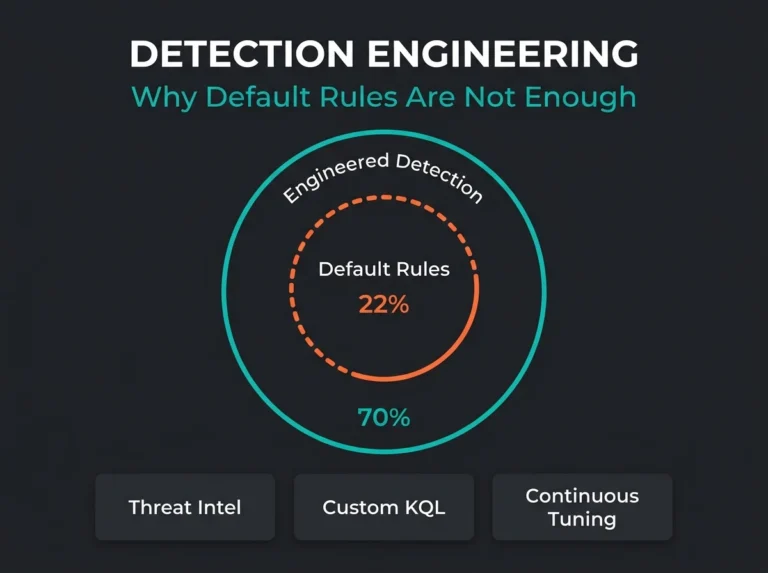
Detection Engineering for Microsoft Sentinel: Why Default Rules Are Not Enough
Default Sentinel rules cover only 22% of MITRE ATT&CK techniques. Learn what detection engineering is and what managed providers do differently.
Read more
What We Find When We Inherit a Client’s Sentinel: A Cost Autopsy
Falconer Security reveals the 5 most common Sentinel cost failures in inherited MSSP workspaces and how to fix them.
Read moreNew Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.