



Microsoft Sentinel
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.
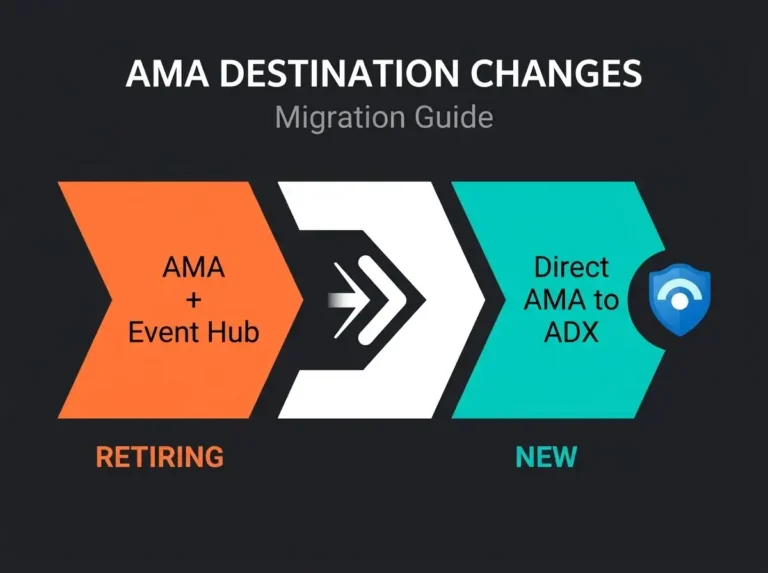
AMA Destination Changes: What Your Sentinel Deployment Needs to Know
Microsoft is retiring AMA Event Hub and Storage destinations in July 2026. Learn how the new direct-to-ADX ingestion works and how to plan your
Read more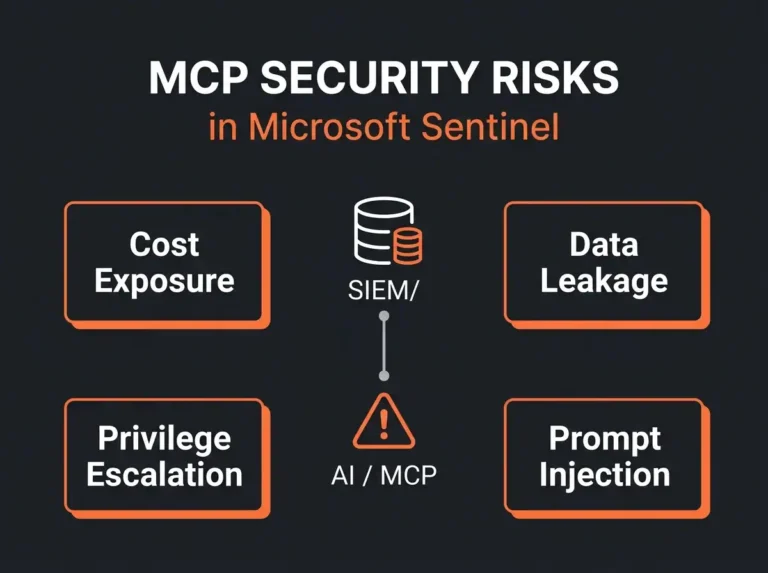
MCP Security Risks in Sentinel: What SOC Teams Need to Know
MCP servers connect AI to Microsoft Sentinel without the guardrails of the Azure portal. Learn the cost, security, and compliance risks – and what
Read more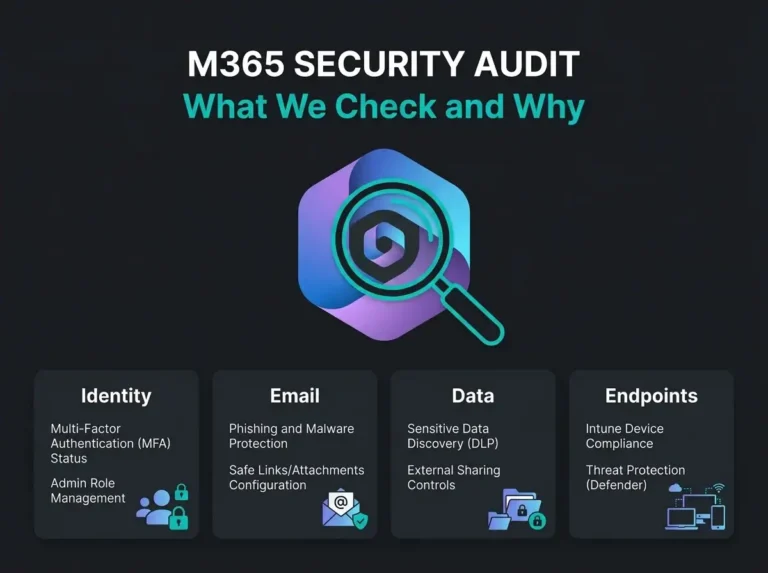
Microsoft 365 Security Audit: What We Check and Why
A Microsoft 365 security audit reviews identity, email, endpoint, data protection, and logging. Learn exactly what we check and what we typically find.
Read more
M365 Security Best Practices for SMBs
Microsoft 365 default settings leave critical security gaps. Learn the essential controls SMBs need: MFA, Conditional Access, email authentication, endpoint protection, and more.
Read moreNew Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.