



Tag
Microsoft 365
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.
Written by practitioners
Microsoft-focused
Actionable advice
30 of 30 articles
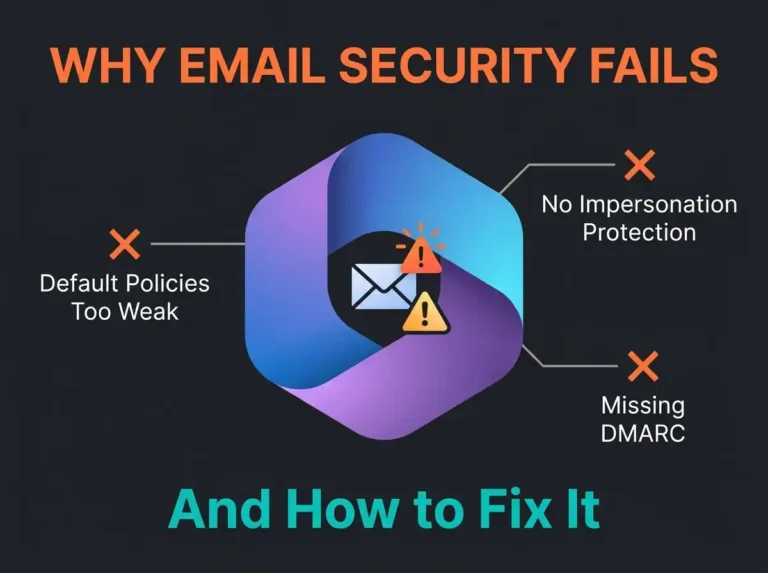
Why Office 365 Email Security Fails (And How to Fix It)
90% of cyberattacks start with email. Despite Microsoft's built-in Exchange Online Protection, sophisticated attacks slip through default settings daily. Here's what actually works to
Read more
MDR vs SIEM: Why You Need Both (And What Each Actually Does)
SIEM is a technology platform (log aggregation and correlation tool). MDR is a service (24/7 security operations team using SIEM and other tools to
Read more
The dispatch
New Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.
We never share your address.