



MDR
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.
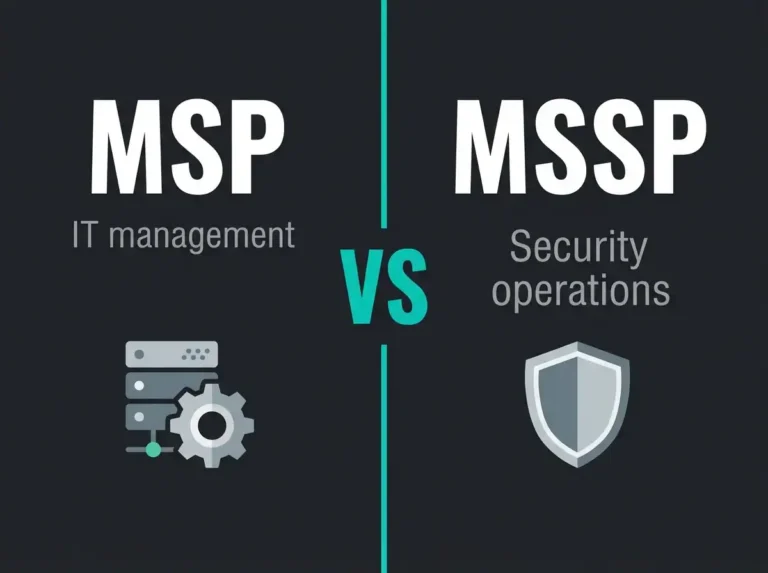
MSP vs MSSP: Which IT Partner Do You Need?
MSPs manage your IT. MSSPs protect it. Learn the key differences in scope, staffing, tools, and cost – and why most SMBs need both.
Read more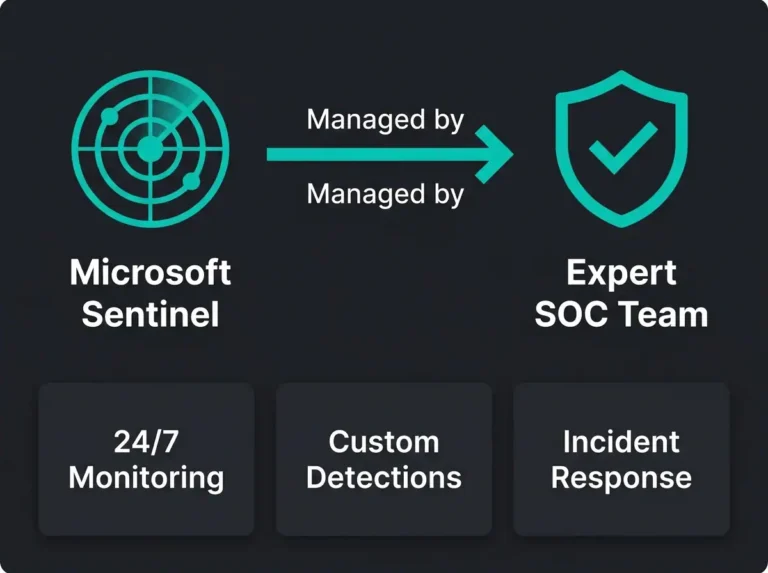
Managed Sentinel Service: Expert SIEM Without Internal SOC Team
You deployed Microsoft Sentinel. Configured data connectors. Enabled pre-built detection rules. Now your security team receives 1,200 alerts daily: 95% false positives, 5% actual
Read more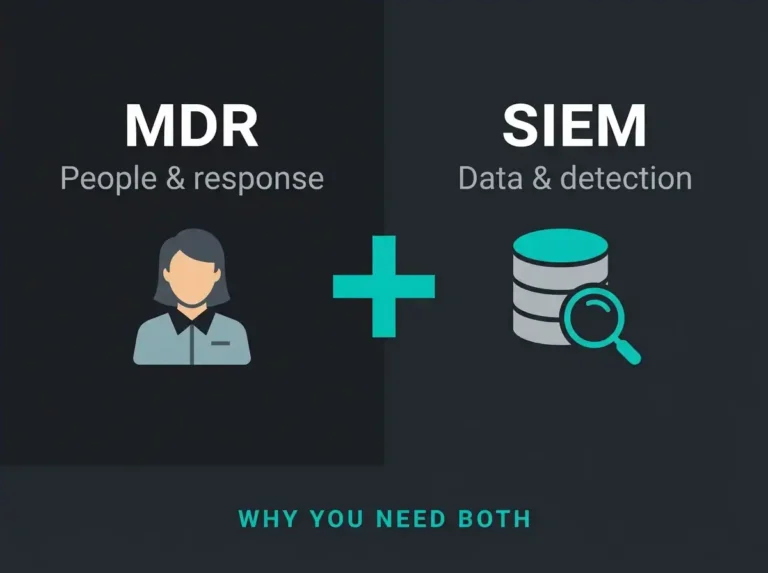
MDR vs SIEM: Why You Need Both (And What Each Actually Does)
SIEM is a technology platform (log aggregation and correlation tool). MDR is a service (24/7 security operations team using SIEM and other tools to
Read moreNew Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.