



Managed SOC
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.

Managed SOC for MSPs: When to Partner Instead of Build
Managed SOC for MSPs: how to choose a SOC partner, define responsibilities, and scale Microsoft-focused security services.
Read more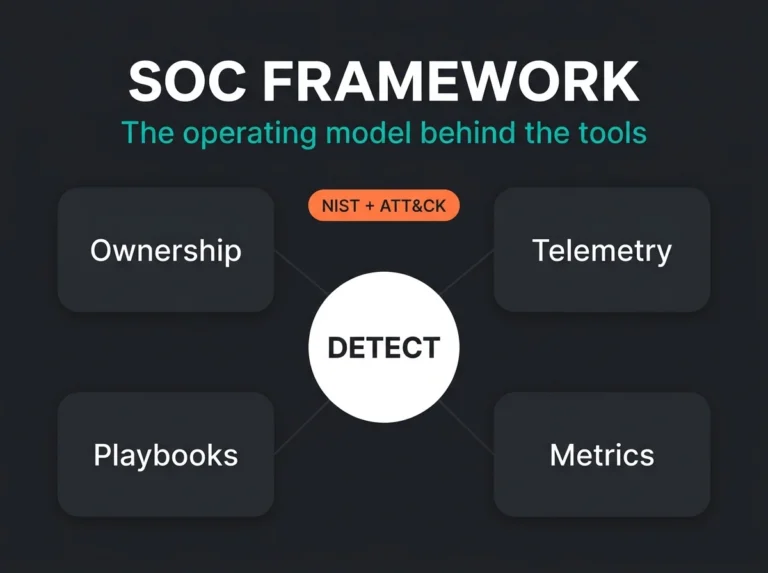
Security Operations Center Framework: What SMBs Actually Need
SOC framework guide for SMBs covering NIST, ATT&CK, detection workflows, response playbooks, and Microsoft security operations design.
Read more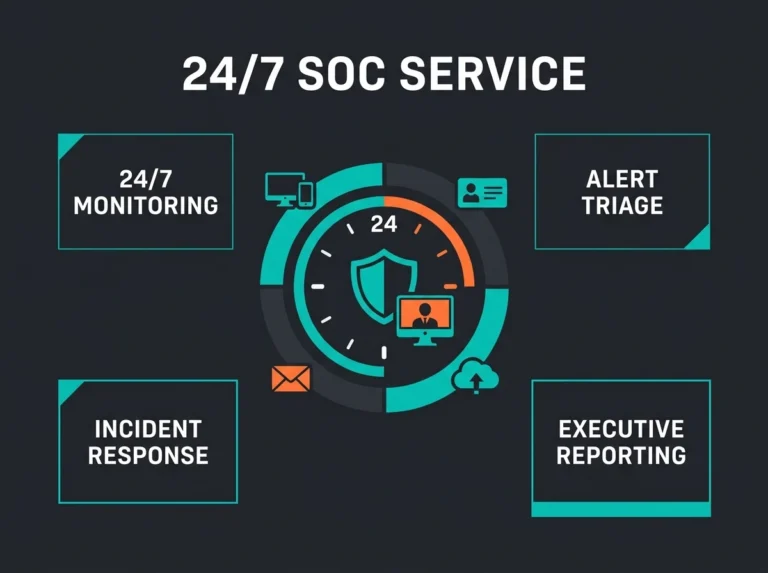
24/7 SOC Service: What Good Coverage Actually Looks Like
24/7 SOC service explained: what continuous monitoring should include, what to ask providers, and when SMBs actually need it.
Read more
SOC as a Service: Complete Guide for SMBs
What SOC as a Service means for SMBs, how it differs from managed SIEM and MDR, and how to evaluate whether an outsourced SOC
Read moreNew Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.