



Tag
Incident Response
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.
Written by practitioners
Microsoft-focused
Actionable advice
2 of 2 articles
24/7 SOC Service: What Good Coverage Actually Looks Like
24/7 SOC service explained: what continuous monitoring should include, what to ask providers, and when SMBs actually need it.
Read more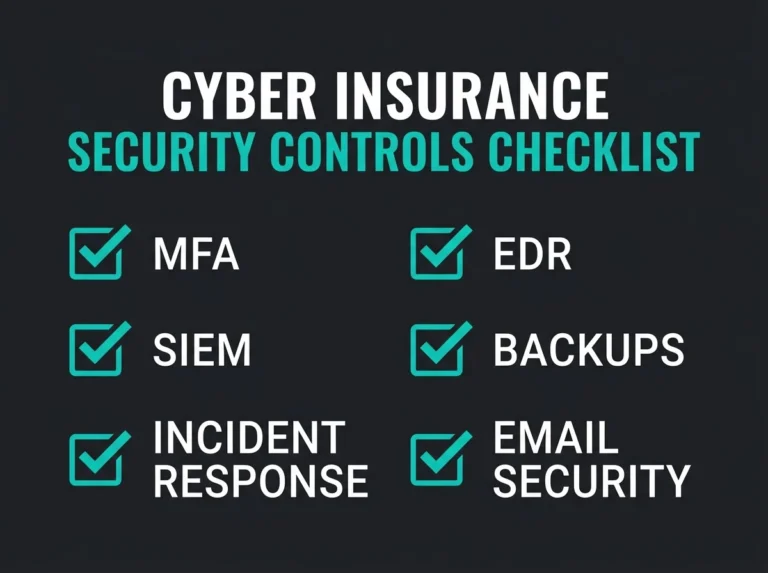
Cyber Insurance Requirements: What Security Controls Do Insurers Require?
Learn the 8 security controls cyber insurers require in 2026, from MFA and EDR to SIEM and incident response plans.
Read more
The dispatch
New Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.
We never share your address.