



Tag
GDAP
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.
Written by practitioners
Microsoft-focused
Actionable advice
2 of 2 articles
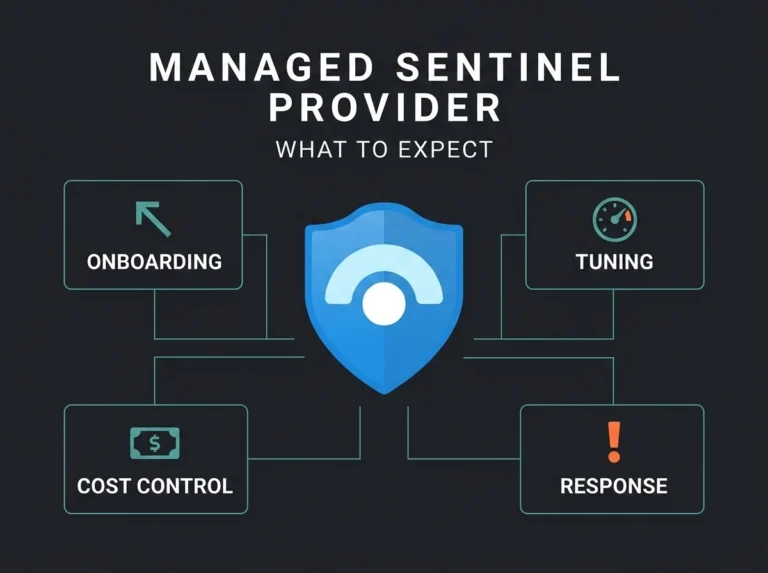
Managed Sentinel Provider: What to Expect
What to expect from a managed Sentinel provider, including onboarding, detection tuning, response workflows, and cost control.
Read more
Deploying Sentinel for a New Client: Our MSSP Onboarding Checklist
Complete MSSP checklist for deploying Microsoft Sentinel. Covers Lighthouse, GDAP, workspace setup, connectors, and cost controls.
Read more
The dispatch
New Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.
We never share your address.