



Microsoft Security Insights
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.
Deploying Sentinel for a New Client: Our MSSP Onboarding Checklist
Complete MSSP checklist for deploying Microsoft Sentinel. Covers Lighthouse, GDAP, workspace setup, connectors, and cost controls.
Read more
Cyber Insurance Requirements: What Security Controls Do Insurers Require?
Learn the 8 security controls cyber insurers require in 2026, from MFA and EDR to SIEM and incident response plans.
Read more
Managed Sentinel Maintenance: What the First 12 Months Actually Look Like
What managed Microsoft Sentinel maintenance looks like month by month. Detection tuning, cost optimization, threat hunting, and reporting.
Read more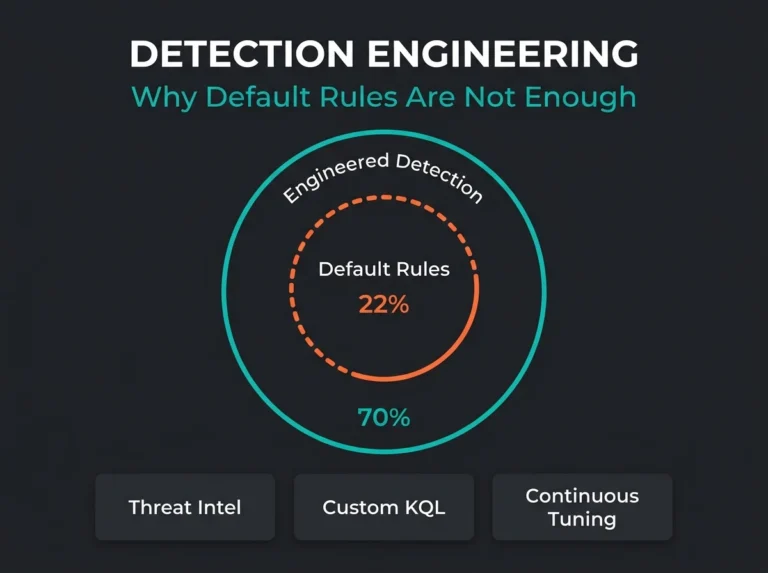
Detection Engineering for Microsoft Sentinel: Why Default Rules Are Not Enough
Default Sentinel rules cover only 22% of MITRE ATT&CK techniques. Learn what detection engineering is and what managed providers do differently.
Read moreNew Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.