



Security Operations
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.

Sentinel SIEM: Features and Capabilities
Sentinel SIEM gives SMBs cloud-native detection, hunting, investigation, and automation, but only if connector, tuning, and cost choices are handled well.
Read more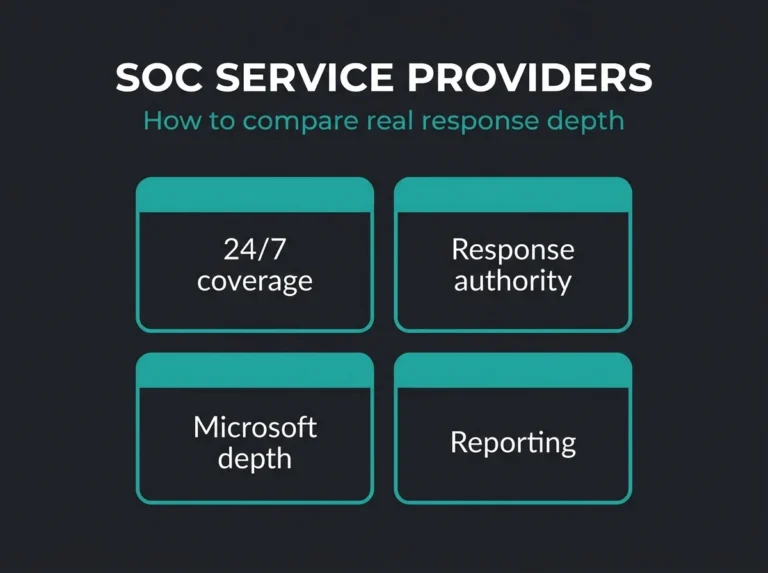
SOC Service Providers: How to Choose
How to compare SOC service providers, response depth, Microsoft fit, and pricing without buying alert forwarding dressed up as a SOC.
Read more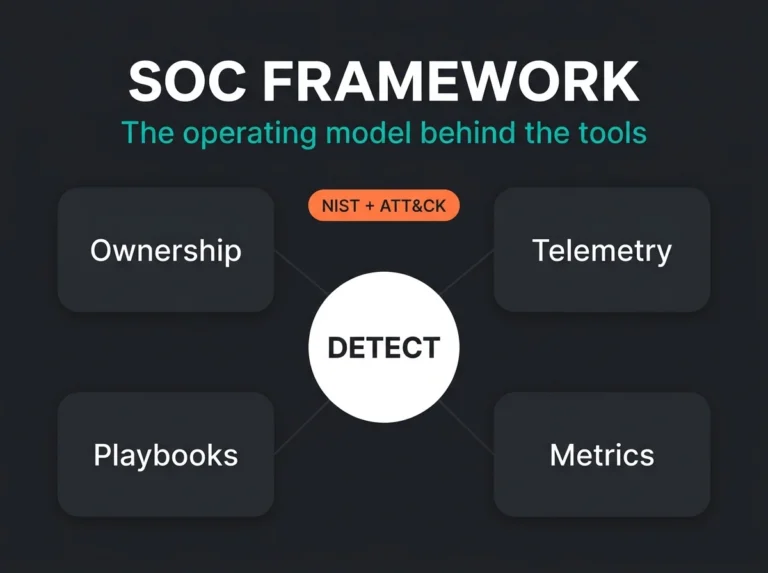
Security Operations Center Framework: What SMBs Actually Need
SOC framework guide for SMBs covering NIST, ATT&CK, detection workflows, response playbooks, and Microsoft security operations design.
Read more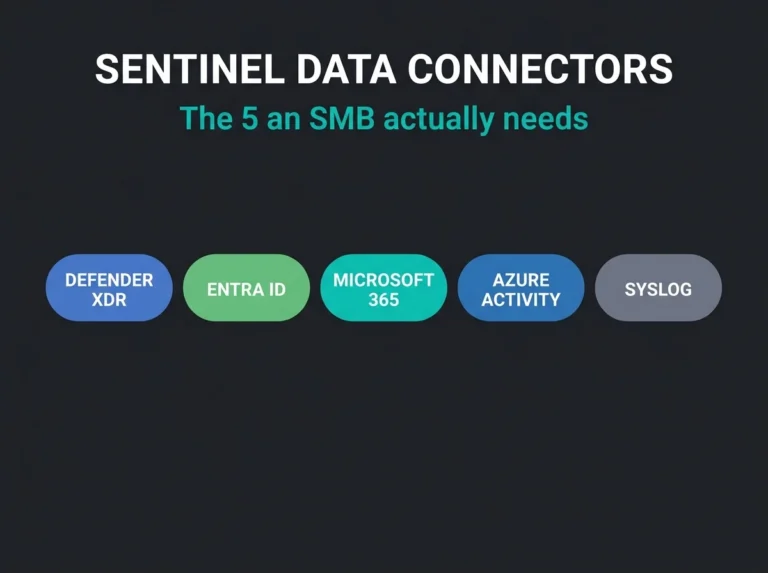
The Only 5 Microsoft Sentinel Data Connectors an SMB Actually Needs
A practical Microsoft Sentinel rollout for SMBs starts with five connectors: Defender XDR, Entra ID, Microsoft 365, Azure Activity, and Syslog via AMA.
Read moreNew Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.