



Insights
Microsoft Security Insights
Practical guidance on Microsoft 365 security, Azure protection, Sentinel SIEM, and managed detection and response. Written by security engineers who configure, harden, and monitor Microsoft environments every day.
Written by practitioners
Microsoft-focused
Actionable advice
6 of 6 articles
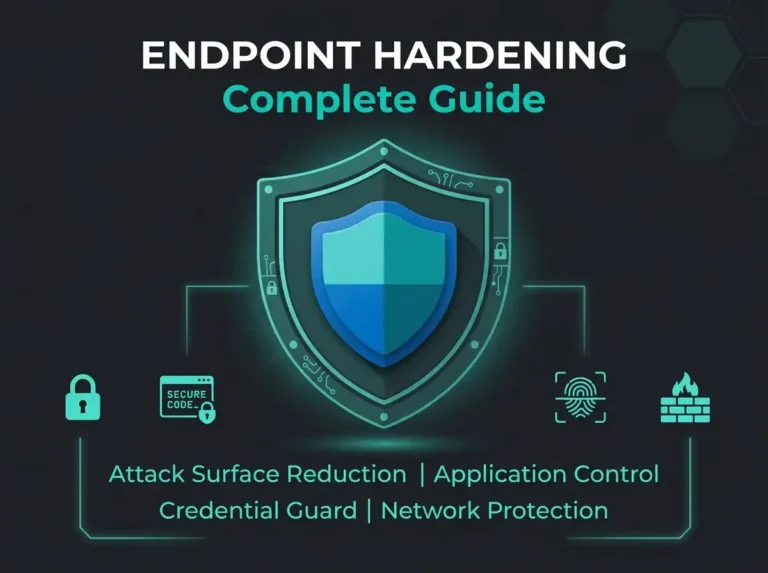
Endpoint Hardening: Complete Guide for Microsoft Environments
Endpoint hardening guide for SMBs running Microsoft 365. 10 best practices using Intune, Defender for Endpoint, and Entra ID.
Read more
Microsoft Defender for Endpoint: Why EDR Beats Traditional Antivirus
Traditional antivirus stops known malware. Endpoint Detection and Response (EDR) stops sophisticated attacks that bypass signature-based detection.
Read more
The dispatch
New Microsoft security guidance, when it lands.
One email when we publish. Practitioner analysis on detection, response, and hardening. No product pitches, unsubscribe anytime.
We never share your address.