



Access & privilege
- Owner and Contributor sprawl across subscriptions
- Standing privileged access vs PIM for Azure roles
- Over-permissioned service principals and managed identities
- Least privilege across management groups

Azure estates drift by default: resources deployed outside the baseline, “temporary” exceptions never reverted, access never removed. A senior engineer maps the few paths an attacker would actually take through yours - not a 400-item recommendation dump.
Cloud misconfiguration is self-inflicted by definition - which means it is also fixable by definition.
Microsoft secures the platform. Your configuration in it is the shared-responsibility half nobody assigned.
Every sprint adds VMs, storage, and roles. Nobody’s job is to look back.
Exceptions, hotfixes, and "temporary" rules have been accumulating ever since.
And the honest answer to "who has Owner?" is a shrug.
Documented and tested against a named benchmark - not assumed.
Plans on that do nothing, plans off that would matter. Both cost you.
of cloud security failures are the customer’s side of the shared-responsibility model - configuration, not platform.
of organisations have already had a cloud data breach - with misconfiguration and human error the #1 root cause.
We don’t hand you 400 recommendations. We map which of your findings chain together into a breach an attacker would actually run - and put those first.
A Secure Score treats every finding as a line item. An attacker treats them as a route - we assess the route.
Six planes of your Azure estate - IaaS, PaaS, containers, and serverless all in scope by default. This is infrastructure; the productivity tenant and Entra ID have their own assessments.
The cloud-security market wants to sell you an enterprise posture platform. But Azure already ships its own: Defender for Cloud’s foundational posture, Secure Score, and the Microsoft Cloud Security Benchmark are free and already running in your tenant - most estates simply never look at them, and never tune the paid plans on top. We make what you own work first.
An assessment is only as strong as what it measures against.
Microsoft’s own security baseline for Azure, auto-assessed by Defender for Cloud and cross-mapped to NIST, ISO 27001, CIS, and PCI. Our findings anchor here - named controls, not opinion.
Auto-assessed · expert-interpretedThe independent hardening standard for Azure, evaluated through the regulatory compliance dashboard. Level 1 for every estate; Level 2 where your risk profile justifies the friction.
Configured in your tenant · evidence stays with youEvery finding carries the compliance references your auditor and insurer ask about, so the report doubles as audit evidence - same format as our other assessments.
EU-first mapping · audit-ready
Same ground rules as every Falconer assessment. Your workloads never notice.
Reader and Security Reader roles - no write access, no changes to resources, no impact on running workloads.
Scoped role assignments you grant and can remove the day we finish. Every read is in your Activity Log.
Defender for Cloud recommendations, Resource Graph queries, and MCSB/CIS evaluation cover the whole estate.
A senior engineer chains findings into attack paths and prioritises ruthlessly. The tooling finds 400 items; we tell you which three matter.
Collection is hours, analysis is days. Findings arrive while they are still true.
Evidence handled under GDPR, stored in the EU, deleted on the schedule we agree.
Same format as our other assessments: an executive summary for the board, remediation-ready findings for engineering, and compliance mapping for the auditor. Azure adds four artifacts of its own.
Where you stand today and the realistic target, so progress is measurable - not a screenshot, a plan.
Every finding by severity, each with the fix - portal steps, CLI, or policy. The 400-item list, put in honest order.
The two or three real chains from the internet to your subscriptions, drawn end to end with the break points.
A per-plan verdict for your estate: what to turn on, what to skip, and what it costs - so the bill matches the risk.
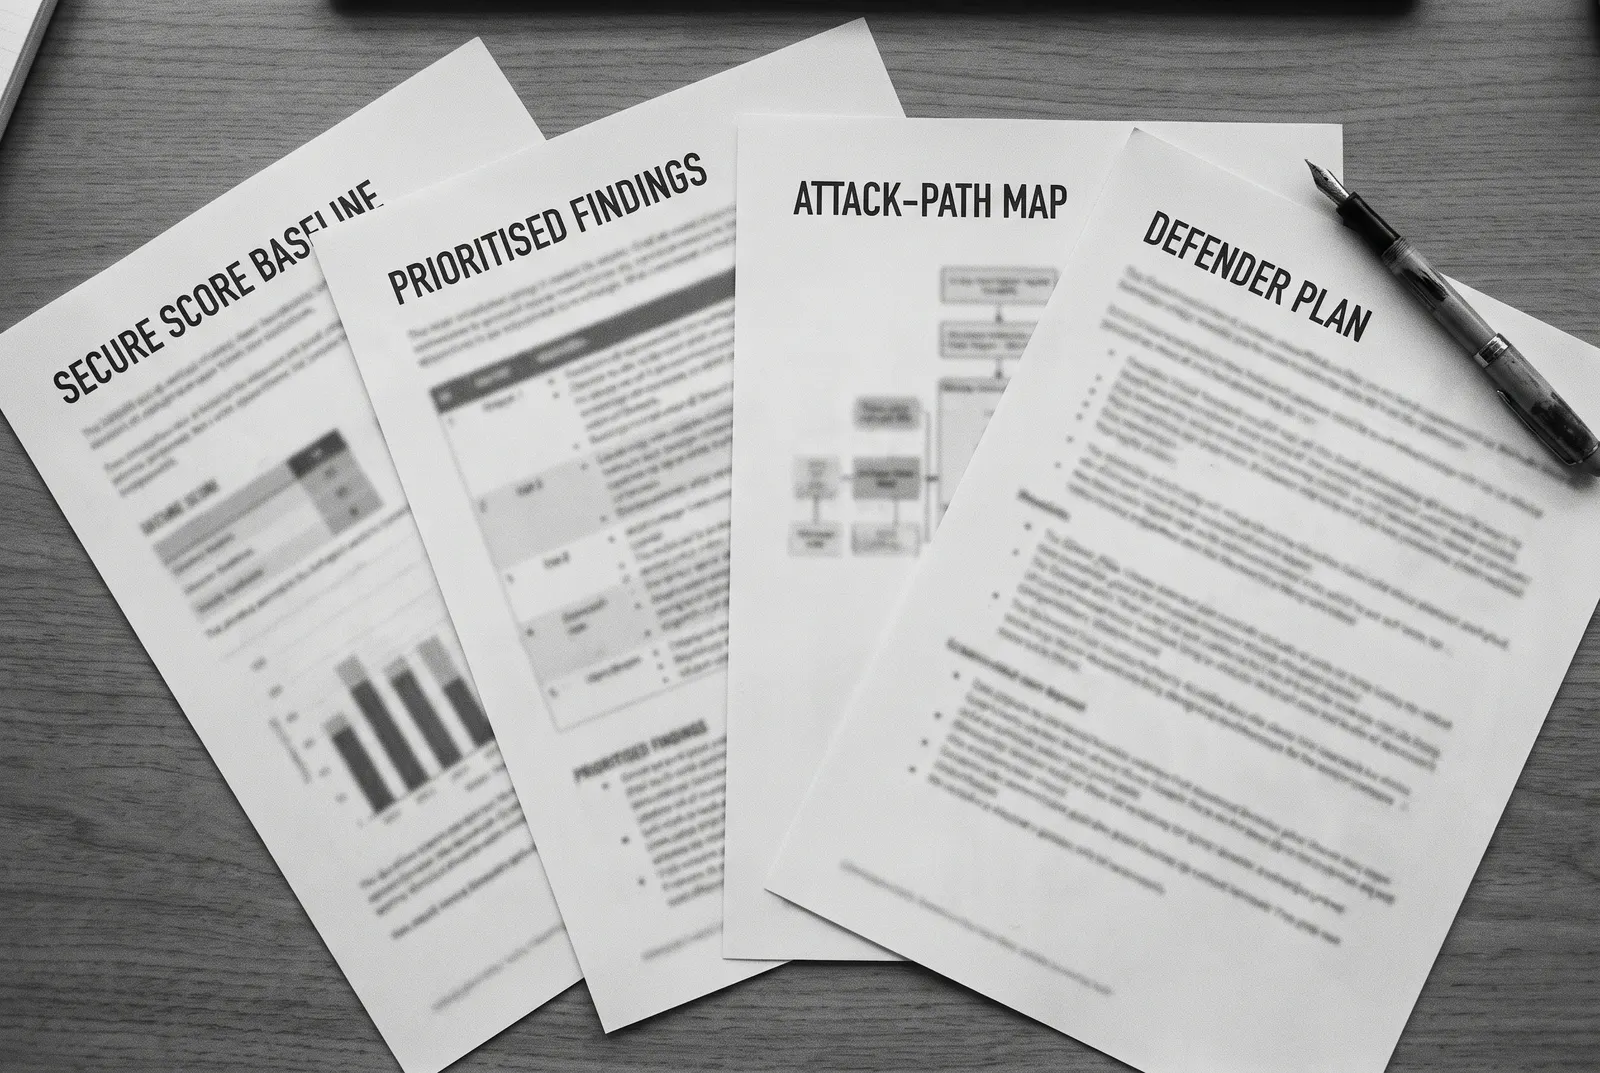
Each artifact is written to be handed on alone - the Defender plan to whoever holds the budget, the attack-path map to your architects - without the rest of the report attached.
Every finding in them carries its own fix - portal steps, CLI, or Azure Policy - so an engineering team can work from the documents without us in the room.
Different domains, different buyers, one report format. Doing two makes sense precisely because the planes connect.
The productivity estate: email, collaboration, data protection, posture. Explore the M365 assessment.
Entra ID: who signs in, Conditional Access, privileged roles. The one link that matters here: a compromised Entra admin can grant themselves Owner across your subscriptions - the directory is the front door to the infrastructure. Explore the identity assessment.
Subscriptions, RBAC, network, storage, Key Vault, compute, logging. Run workloads in AWS or GCP too? Defender for Cloud can extend there - we stay Azure-first and scope multicloud honestly when asked.
Find, fix, watch - and the report stands alone whichever parts you take.
Portal steps, CLI, or Azure Policy, per finding. Many engineering teams remediate in-house with the report alone.
We close the attack paths and the top findings, stand up the policy guardrails, and hand the estate back measurably harder.
Posture is a snapshot of a thing that drifts. Managed Sentinel ingests your Activity logs and Defender for Cloud alerts; MDR watches the workloads around the clock. Explore Managed Sentinel and MDR.
Microsoft secures the platform: the datacenters, the hypervisors, the physical network. Everything you deploy on it - access, network rules, storage exposure, secrets - is your side of the shared-responsibility model. Industry analysis consistently attributes the overwhelming majority of cloud security failures to customer configuration, not the platform.
Six planes: access and privilege (RBAC, PIM, service principals), network exposure, storage and data, Key Vault and secrets, compute and workloads (VMs, AKS, serverless), and logging and governance. All workload types are in scope by default; the scope section above lists the specific checks.
No. Reader and Security Reader roles only - read-only by design, granted by you, removable by you the day we finish. Every read we make lands in your Activity Log.
Secure Score treats every finding as an independent line item. An attacker treats your findings as a route. The value of the assessment is the correlation: which of your 400 recommendations chain together into the two or three real paths from the internet to subscription owner - and closing those first.
At SMB and mid-market scale, usually not. Defender for Cloud is the native posture platform - the foundational tier is free and already on - and it covers what a CNAPP is sold to cover for a single-cloud Azure estate. We make it work before anyone buys anything.
That is a named deliverable: the Defender-plan right-sizing review. Plans are priced per resource, so the honest answer depends on your estate - which workloads face the internet, what the data is worth, what you already license. The report gives a per-plan verdict with the monthly cost next to the risk it buys down.
We are Azure-first. Defender for Cloud can extend posture management to AWS and GCP, and if part of your estate lives there we will say honestly whether that extension is worth it - but this assessment, and our depth, is Azure.
Different planes. M365 covers the productivity tenant, identity covers Entra ID and who signs in, this covers the infrastructure your workloads run on. They connect - a compromised Entra admin can escalate into the Azure resource plane - which is exactly why they are assessed separately but designed to pair.
Yes. Findings anchor to the Microsoft Cloud Security Benchmark and CIS Azure Foundations Benchmark, and every finding carries NIS2, ISO 27001, and GDPR references where relevant - so the report doubles as audit and insurance evidence.
Your choice. Every finding ships with the fix, so your engineers can remediate in-house. If you want help, we offer scoped hardening - and because Azure drifts, the natural next step for many is continuous monitoring through Managed Sentinel and MDR.
Days, not weeks: collection is hours, expert analysis takes a few days. It is a fixed-fee engagement sized by your estate - subscriptions, resource count, workload mix - and quoted before we start.
A Microsoft security specialist reads every message and replies, usually within one business day. Whether you need monitoring, help with a specific tool, or just have a question, start here.
New to this? Ask about a free Microsoft security review as a starting point.
"*" indicates required fields